

Essentials Practice Dumps - Verified By DumpExam Updated 75 Questions
Updated Essentials Exam Dumps - PDF Questions and Testing Engine
NEW QUESTION 30
After you enable spamBlocker, your users experience no reduction in the amount of spam they receive. What could explain this? (Select three.)
- A. The Maximum File Size to Scan option is set too high.
- B. Connections cannot be resolved to the spamBlocker servers because DNS is not configured onthe Firebox.
- C. The spamBlocker action for Confirmed Spam is set to Allow.
- D. spamBlocker Virus Outbreak Detection is notenabled.
- E. A spamBlocker exception is configured to allow traffic fromsender *.
Answer: B,C,E
Explanation:
A: Spamblocker requires DNS to be configured on your XTM device
B: If you use spamBlocker with the POP3 proxy, you have only two actions to choose from: Add Subject Tag and Allow. Allow lets spam email messages go through theFirebox without a tag.
D: The Firebox might sometimes identify a message as spam when it is not spam. If you know the address of the sender, you can configure the Firebox with an exception that tells it not to examine messages from that source address or domain.
Reference: Fireware Basics, Courseware: WatchGuard System Manager 10, page 138
NEW QUESTION 31
With the policies configured as shown in this image, HTTP traffic can be sent and received through branch office VPN tunnel.1 and tunnel.2.
- A. False
- B. True
Answer: B
NEW QUESTION 32
Match each WatchGuard Subscription Service with its function.
Uses rules, pattern matching, and sender reputation to block unwanted email messages. (Choose one).
- A. Spam Blocker
- B. APTBlocker
- C. Gateway / Antivirus
- D. Reputation Enable Defense RED
- E. Intrusion Prevention Server IPS
Answer: A
Explanation:
SpamBlocker provides a spam scanning engine that works in concert with WatchGuard's cloud-based technology to prevent spam from gaining access to the email servers (and clients).
Reference:http://www.tomsitpro.com/articles/network-security-solutions-guide, 2-866-6.html
NEW QUESTION 33
Match each type of NAT with the correct description:
Conserves IP addresses and hides the internal topology of your network. (Choose one)
- A. 1-to1 NAT
- B. Dynamic NAT
- C. NAT Loopback
Answer: B
Explanation:
Explanation/Reference:
Dynamic NAT is also known as IP masquerading. With dynamic NAT many computers can connect to the Internet from one public IP address. Dynamic NAT gives more security for internal hosts that use the Internet, because it hides the IP addresses of hosts on your network.
Reference: http://www.watchguard.com/help/docs/wsm/xtm_11/en-US/index.html#en-US/nat/ nat_dynamic_use_c.html%3FTocPath%3DNetwork%2520Address%2520Translation%2520(NAT)%
7CAbout%2520Dynamic%2520NAT%7C_____0
NEW QUESTION 34
Match each type of NAT with the correct description:
Conserves IP addresses and hides the internal topology of your network. (Choose one)
- A. 1-to1 NAT
- B. Dynamic NAT
- C. NAT Loopback
Answer: B
Explanation:
Explanation/Reference:
Dynamic NAT is also known as IP masquerading. With dynamic NAT many computers can connect to the Internet from one public IP address. Dynamic NAT gives more security for internal hosts that use the Internet, because it hides the IP addresses of hosts on your network.
Reference: http://www.watchguard.com/help/docs/wsm/xtm_11/en-US/index.html#en-US/nat/ nat_dynamic_use_c.html%3FTocPath%3DNetwork%2520Address%2520Translation%2520(NAT)%7CAbout%
2520Dynamic%2520NAT%7C_____0
NEW QUESTION 35
Match each WatchGuard Subscription Service with its function.
Manages use of applications on your network. (Choose one).
- A. APT Blocker
- B. Application Control
- C. Reputation Enable Defense RED
- D. Intrusion Prevention Server IPS
- E. Data Loss Prevention DLP
Answer: B
Explanation:
Application Control keeps unproductive,inappropriate, and dangerous applications off-limits.
Stay on top of the applications running on your network for tight security and high productivity with a subscription to WatchGuard Application Control. It allows you to establish which applications canbe used within your organization, by whom, and when.
Reference:http://www.watchguard.com/docs/brochure/wg_application-control_ds.pdf
NEW QUESTION 36
You have a privately addressed email server behind your Firebox. If you want to make sure that all traffic from this server to the Internet appears to come from the public IP address 203.0.113.25, regardless of policies, which from of NAT would you use? (Select one.)
- A. In the SMTP policy that handles traffic from the email server, select the option to apply dynamic NAT to all traffic in the policy and set the source IP address 203.0.113.25.
- B. Create a global dynamic NAT rule for traffic from the email server and set the source IP address to
203.0.113.25. - C. Create a static NAT action for traffic to the email server, and set the source IP address to 203.0.113.25.
Answer: B
NEW QUESTION 37
Match each type of NAT with the correct description:
Conserves IP addresses and hides the internal topology of your network. (Choose one)
- A. 1-to1 NAT
- B. Dynamic NAT
- C. NAT Loopback
Answer: B
NEW QUESTION 38
Only 50 clients on the trusted network of your Firebox can connect to the Internet at the same time. What could cause this? (Select one.)
- A. The device feature key allows a maximum of 50 client connections.
- B. The DHCP address pool on the trusted interface has only 50 IP addresses.
- C. The Outgoing policy allows a maximum of 50 client connections.
- D. TheLiveSecurity feature key is expired.
Answer: B
NEW QUESTION 39
With the policies configured as shown in this image, HTTP traffic can be sent and received through branch office VPN tunnel.1 and tunnel.2.
- A. False
- B. True
Answer: A
NEW QUESTION 40
In the default Firebox configuration file, which policies control management access to the device? (Select two.)
- A. FTP
- B. Outgoing
- C. WatchGuard Web UI
- D. WatchGuard
- E. Ping
Answer: D,E
Explanation:
When you configure the Firebox with the Quick Setup Wizard, the wizard adds four basic policies: TCP/UDP outgoing, FTP packet filter, ping, and WatchGuard.
Reference: Fireware Basics, Courseware: WatchGuard System Manager 10, page 15
NEW QUESTION 41
Users on the trusted network cannot browse Internet websites. Based on the configuration shown in this image, what could be the problem with this policy configuration? (Select one.)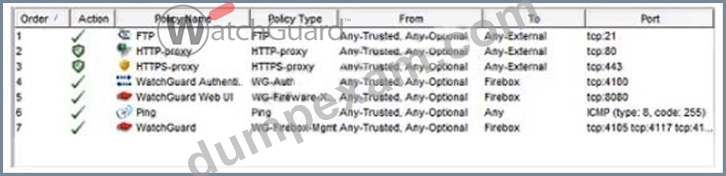
- A. The HTTP-proxy allows Any-Trusted and Any-Optional to Any-External.
- B. The HTTP-proxy policy is configured for the wrong port.
- C. The HTTP-proxy policy has higher precedence than the HTTPS-proxy policy.
- D. The default Outgoingpolicy has been removed and there is no policy to allow DNS traffic.
Answer: B
NEW QUESTION 42
In the default Firebox configuration file, which policies control management access to the device? (Select two.)
- A. FTP
- B. Outgoing
- C. WatchGuard
- D. Ping
- E. WatchGuard Web UI
Answer: C,E
Explanation:
Ping is generated by default as the explanation states but Ping does not manage the device. The policies that manage the device are WatchGuard & WatchGuard Web UI
NEW QUESTION 43
From the Firebox System Manager >Authentication List tab, you can view all of the authenticated users connected to your Firebox and disconnect any of them.
- A. False
- B. True
Answer: B
NEW QUESTION 44
How is a proxy policy different from a packet filter policy? (Select two.)
- A. Only a proxy policy uses the IP source,destination, and port to control network traffic.
- B. Only a proxy policy can prevent specific threats without blocking the entire connection.
- C. Only a proxy works at the application, network, and transport layers to examine all connection data.
- D. Only a proxy policy examines information in the IP header.
Answer: B,C
Explanation:
C: Proxies can prevent potential threats from reaching your network without blocking the entire connection.
D: A proxy operates at the application layer, as well as the network and transport layers of a TCP/IP packet, while a packet filter operates onlyat the network and transport protocol layers.
Incorrect:
Not A: A packet filter examines each packet's IP header to control the network traffic into and out of your network.
Reference: Fireware Basics, Courseware: WatchGuard System Manager 10, page 95
NEW QUESTION 45
Match the monitoring tool to the correct task.
Which is not a Fireware monitoring tool? (Select one)
- A. Traffic Monitor
- B. Firebox System Manager - Subscription services
- C. FireWatch
- D. FireBox System Manager - Blocked Sites list
- E. Log Server
- F. Firebox System Manager - Authentication list
Answer: E
Explanation:
The Fireware monitor and configuration tools are: Edge Web Manager, Firebox System Manager, HostWatch, and Ping.
Reference: Fireware Basics, Courseware: WatchGuard System Manager 10, pages 15, 34, 59,
NEW QUESTION 46
Users on the trusted network cannot browse Internet websites. Based on the configuration shown in this image, what could be the problem with this policy configuration? (Select one.)
- A. The HTTP-proxy allows Any-Trusted and Any-Optional to Any-External.
- B. The default Outgoing policy has been removed and there is no policy to allow DNS traffic.
- C. The HTTP-proxy policy has higher precedence than the HTTPS-proxy policy.
- D. The HTTP-proxy policy is configured for the wrong port.
Answer: B
NEW QUESTION 47
When your device is in a default state, to which interface do you connect your management computer so you can use the Quick Setup Wizard or Web Setup Wizard to configure the device? (Select one.)
- A. Any interface
- B. Console interface
- C. Interface 1
- D. Interface 0
Answer: C
Explanation:
Explanation/Reference:
To start the Web Setup Wizard, connect your computer to interface number 1 of your XTM device with an Ethernet cable. This is the trusted interface.
Reference: http://www.watchguard.com/help/docs/wsm/xtm_11/en-US/index.html#en-US/installation/ qsw_web_about_c.html
NEW QUESTION 48
Which items are included in a Firebox backup image? (Select four.)
- A. Log file
- B. Feature keys
- C. Support snapshot
- D. Certificates
- E. Fireware OS
- F. Configuration file
Answer: B,D,E,F
Explanation:
A Firebox backup imageis a saved copy of the working image from the Firebox flash disk. The backup image includes the Firebox appliance software, configuration file, licenses, and certificates.
When you purchase an option for your Firebox, you add a new feature key to your configuration file.
Reference: Fireware Basics, Courseware: WatchGuard System Manager 10, pages 14, 57
NEW QUESTION 49
Match the monitoring tool to the correct task.
Which tool can view a list of users connected to the Firebox? (Select one)
- A. Log Server
- B. Firebox System Manager - Authentication list
- C. Traffic Monitor
- D. Firebox System Manager - Subscription services
- E. FireWatch
- F. FireBox System Manager - Blocked Sites list
Answer: B
Explanation:
Explanation/Reference:
You can view a list of users connected to the Firebox through HostWatch, and you can also use Authentication List, which identifies the IP addresses and user names of all the users that are authenticated to the Firebox.
Reference: Fireware Basics, Courseware: WatchGuard System Manager 10, pages 15, 34, 59, 181
NEW QUESTION 50
HOTSPOT
Match each type of NAT with the correct description:
Answer:
Explanation:
Explanation:
NAT Loopback 1-to 1 NAT
Dynamic NAT
NEW QUESTION 51
You can use Firebox System Manager to download a PCAP file that includes packet information about the protocols that manage traffic on your network.
- A. False
- B. True
Answer: B
NEW QUESTION 52
When your users connect to the Authentication Portal page to authenticate, they see a security warning message in their browses, which they must accept before they can authenticate. How can you make sure they do not see this security warning message in their browsers? (Select one.)
- A. Import a custom self-signed certificate or a third-party certificate to your Firebox and import the same certificate to all client computers or web browsers.
- B. Add the user accounts for your users who use the Authentication Portal to a list of trusted users on your Firebox.
- C. Instruct them to disable security warning message in their preferred browsers.
- D. Replace the Firebox certificate with the trusted certificate from your web server.
Answer: A
NEW QUESTION 53
For which of these third party authentication methods must you specify a search base? (Select two.)
- A. LDAP
- B. Active Directory
- C. RADIUS
- D. SecurID
Answer: A,B
Explanation:
B: Configuring the Firebox to use Active Directory authentication is similar to the process for LDAP authentication. You must set a search base to put limits on the directories on the authentication server the Firebox searchesin for an authentication match.
D: When you configure the Firebox to use LDAP authentication, you must set a search base to put limits on the directories on the authentication server the Firebox searches in for an authentication match
Reference: FirewareBasics, Courseware: WatchGuard System Manager 10, page 83-84
NEW QUESTION 54
If your Firebox has a single public IP address, and you want to forward inbound traffic to internal hosts based on the destination port, which type of NAT should you use? (Select one.)
- A. 1-to-1 NAT
- B. Static NAT
- C. Dynamic NAT
Answer: A
NEW QUESTION 55
......
How to book the Essential Exam
These are following steps for registering the Essential exam.
- Step 1: Visit to WatchGaurd Exam Registration
- Step 2: Sign up/Login to WatchGaurd account
- Step 3: Select local centre based on your country, date, time and confirm with a payment method.
New (2021) WatchGuard Essentials Exam Dumps: https://www.dumpexam.com/Essentials-valid-torrent.html
Best Way To Study For WatchGuard Essentials Exam Brilliant Essentials Exam Questions PDF: https://drive.google.com/open?id=1XVsKwFrAY0Gau1rvgzbzxh62yp9vSaFW
